Instant Download: Upon successful payment, Our systems will automatically send the product you have purchased to your mailbox by email. (If not received within 12 hours, please contact us. Note: don't forget to check your spam.)
Instant Download CompTIA : SY0-701日本語 Questions & Answers as PDF & Test Engine

- Exam Code: SY0-701
- Exam Name: CompTIA Security+ Certification Exam (SY0-701日本語版)
- Updated: Nov 14, 2026
- No. of Questions: 916 Questions and Answers
- Download Limit: Unlimited

Price: $79.98
- Online Tool, Convenient, easy to study.
- Instant Online Access SY0-701日本語 Dumps
- Supports All Web Browsers
- SY0-701日本語 Practice Online Anytime
- Test History and Performance Review
- Supports Windows / Mac / Android / iOS, etc.
Price: $79.98
- Installable Software Application
- Simulates Real SY0-701日本語 Exam Environment
- Builds SY0-701日本語 Exam Confidence
- Supports MS Operating System
- Two Modes For SY0-701日本語 Practice
- Practice Offline Anytime

Price: $79.98
- Printable SY0-701日本語 PDF Format
- Prepared by CompTIA Experts
- Instant Access to Download SY0-701日本語 PDF
- Study Anywhere, Anytime
- 365 Days Free Updates
- Free SY0-701日本語 PDF Demo Available
Everything after 'I want to certify' lives in one place at Lead2Passed: a free demo, instant delivery, study-anywhere formats, 365 days of free updates, and a money back guarantee with published conditions. The 916 practice questions for the SY0-701日本語 exam are the core; the service around them covers the rest of your CompTIA Security+ Certification Exam (SY0-701日本語版) journey.
CompTIA SY0-701日本語 Exam Overview:
| Certification Vendor: | CompTIA |
|---|---|
| Exam Name: | CompTIA Security+ Certification Exam |
| Exam Number: | SY0-701 |
| Exam Price: | $370 USD |
| Available Languages: | Japanese, English, Portuguese, Spanish |
| Real Exam Qty: | Maximum 90 |
| Exam Duration: | 90 minutes |
| Passing Score: | 750 (scale of 100-900) |
| Exam Format: | Performance-based questions (PBQs), Multiple-choice (single and multiple response) |
| Certificate Validity Period: | 3 years |
| Related Certifications: | CompTIA CySA+ CompTIA A+ CompTIA Network+ CompTIA CASP+ |
| Sample Questions: | DOWNLOAD DEMO |
| Exam Way: | Pearson VUE testing centers (in-person) |
| Pre Condition: | Recommended: CompTIA Network+ and 2 years of experience in IT administration with a security focus. Not required but highly recommended. |
| Official Syllabus URL: | https://www.comptia.org/certifications/security#examdetails |
CompTIA SY0-701日本語 Exam Syllabus Topics:
| Section | Weight | Objectives |
|---|---|---|
| Topic 1: Governance, Risk & Compliance | 14% | - Explain privacy and sensitive data concepts in relation to security
|
| Topic 2: Implementation | 25% | - Given a scenario, implement cybersecurity resilience solutions
|
| Topic 3: Threats, Attacks & Vulnerabilities | 24% | - Explain penetration testing and vulnerability scanning concepts
|
| Topic 4: Architecture & Design | 21% | - Explain the importance of embedded and specialized systems security
|
| Topic 5: Operations & Incident Response | 16% | - Given a scenario, apply incident response and recovery procedures
|
The SY0-701日本語 Exam, Explained: Your Top Questions
On delivery: the download is available the moment your payment clears, and a copy reaches your email within one minute. If 2 hours pass and nothing arrives, check spam and contact our support team. Install the software on as many computers as you need — there is no device limit.
On outcomes: if you take the SY0-701日本語 exam within 60 days of purchase and do not pass, the Lead2Passed money back guarantee applies. File your claim within 2 days of the exam with a scanned enrollment slip and the official score report (PDF); claims are processed within 7 days. The candidate name must match the payer name, and the policy excludes exams taken within 3 days of purchase, purchases never used in an actual exam attempt, free materials, and expired orders. Alternatively, you can exchange the product for two free exam packages of equal value and keep the update service on your original purchase.
The SY0-701日本語 exam gives you 90 minutes to work through Maximum 90 questions. That pace punishes perfectionism — the candidates who struggle are usually the ones who burned ten minutes on one stubborn item. Train the skill directly: take timed, full-length mocks in the Lead2Passed desktop or online test engine, practice skipping and returning, and walk in with a pacing strategy you have already tested.
Recommended: CompTIA Network+ and 2 years of experience in IT administration with a security focus. Not required but highly recommended.
Vendor requirements do change, so before you commit to an exam date, confirm the latest eligibility rules on the official CompTIA exam page.
The CompTIA Security+ Certification Exam (SY0-701日本語版) syllabus is split into 5 domains, anchored by Governance, Risk & Compliance (14%), Threats, Attacks & Vulnerabilities (24%), and Implementation (25%). The full breakdown sits in the syllabus section above — treat it as the checklist that decides where your study hours go.
The passing mark for the SY0-701日本語 exam is 750 (scale of 100-900), and the official registration fee is $370 USD. Remember that the fee covers a single attempt — fail, and the retake costs the same again with no loyalty discount. Protect the budget by self-testing first: drill 916 practice questions at Lead2Passed under timed conditions until your scores clear the bar with margin, then register.
The SY0-701日本語 exam, officially the CompTIA Security+ Certification Exam (SY0-701日本語版), is CompTIA's benchmark for proving you can work with its technologies in professional settings; passing it awards the CompTIA Security+ certification, which sits at the Entry-Level level. Because the credential is issued by the vendor itself, it carries weight with employers that self-assessed skills simply cannot match. It also opens the road toward CompTIA A+, CompTIA Network+, CompTIA CySA+, CompTIA CASP+.
Yes — Lead2Passed publishes a free PDF demo of the SY0-701日本語 materials so you can check the question quality and verified answers before paying anything. Once you purchase, 365 days of free updates come standard, and if your product expires you can renew the update service at a 50% discount from your member zone.
CompTIA Security+ Certification Exam (SY0-701日本語版) Sample Questions:
セキュリティ アナリストは、ネットワークに接続されている現在のエンドポイント資産の月次監査中に不正なデバイスを発見しました。企業ネットワークは、アクセス制御に 002.1X を使用しています。デバイスがネットワークにアクセスするには、既知のハードウェア アドレスを持ち、有効なユーザー名とパスワードをキャプティブ ポータルに入力する必要があります。監査レポートは次のとおりです。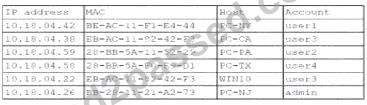
不正なデバイスの接続が許可される可能性が最も高い方法はどれですか?
- A. DNS ハイジャックにより、攻撃者はキャプティブ ポータルのトラフィックを傍受できます。
- B. 管理者がテストのためにセキュリティ制御をバイパスしました。
- C. DMCP障害により誤ったIPアドレスが配布されました
- D. ユーザーが個人のデバイスを使用して MAC クローン攻撃を実行しました。
Correct Answer: D 🗳️
Explanation: Only visible for Lead2Passed members. You can sign-up / login (it's free).
セキュリティ戦略において欺瞞技術を使用する目的を最も適切に説明しているのは、次のうちどれですか?
- A. エンドポイント保護ツールによるマルウェアのインストールを防止する
- B. 攻撃者を管理された環境に誘い込み、脅威情報を収集する
- C. 特権ユーザーアカウントを監視することで内部脅威を検出する
- D. 重要な情報システムに到達する前に、すべての外部トラフィックをブロックする。
Correct Answer: B 🗳️
Explanation: Only visible for Lead2Passed members. You can sign-up / login (it's free).
次のどれが CVSS の使用例ですか?
- A. システムのパッチ適用に関連するコストを決定する
- B. コードを分析して、悪用される可能性のある欠陥を見つける
- C. 使用されていないポートと閉じるべきサービスを識別する
- D. 脆弱性の修復を優先する
Correct Answer: D 🗳️
Explanation: Only visible for Lead2Passed members. You can sign-up / login (it's free).
インフラストラクチャの展開を自動化しようとする組織では、次のテクノロジのどれを使用する必要がありますか?
- A. IoT
- B. IaC
- C. IaaS
- D. IoC
Correct Answer: B 🗳️
Explanation: Only visible for Lead2Passed members. You can sign-up / login (it's free).
侵入テスト担当者は、エンゲージメント ルールに従ってクライアント環境に対してポートおよびサービスのスキャンを実行することでエンゲージメントを開始します。テスト担当者が実行する偵察の種類は次のどれですか。
- A. アクティブ
- B. 攻撃的
- C. 防御的
- D. パッシブ
Correct Answer: A 🗳️
Explanation: Only visible for Lead2Passed members. You can sign-up / login (it's free).
Viewing page 1 out of 184 pages.
Viewing questions 1-5 out of 916 questions.
100% Money Back Guarantee
Lead2Passed has an unprecedented 99.6% first time pass rate among our customers.  We're so confident of our products that we provide no hassle product exchange.
- Best exam practice material
- Three formats are optional
- 10 years of excellence
- 365 Days Free Updates
- Learn anywhere, anytime
- 100% Safe shopping experience
Over 56368+ Satisfied Customers

 0 Customer Reviews