New NSE5_EDR-5.0 Test Materials & Valid NSE5_EDR-5.0 Test Engine
NSE5_EDR-5.0 Updated Exam Dumps [2023] Practice Valid Exam Dumps Question
The Fortinet NSE 5 - FortiEDR 5.0 certification exam is a 60-minute test that consists of 35 multiple-choice questions. NSE5_EDR-5.0 exam is available in English and can be taken either online or at a Pearson VUE testing center.
Candidates who wish to take the Fortinet NSE5_EDR-5.0 exam must have a basic understanding of endpoint security and network security concepts. Candidates must also have experience in the deployment, management, and troubleshooting of FortiEDR 5.0. Candidates who have completed the Fortinet NSE4 certification are recommended to take NSE5_EDR-5.0 exam.
NEW QUESTION # 17
Refer to the exhibit.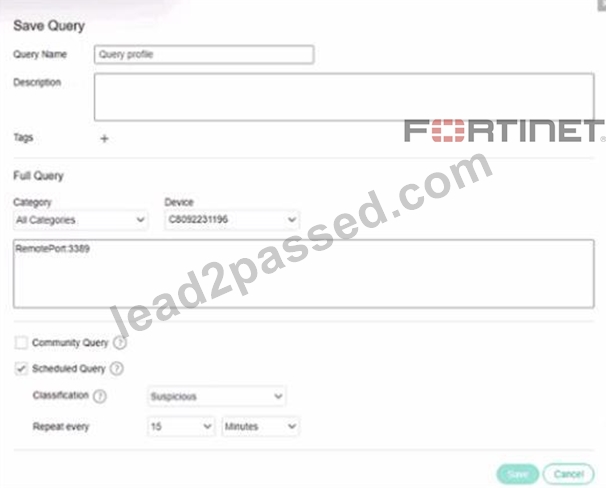
Based on the threat hunting query shown in the exhibit which of the following is true?
- A. The query will only check for network category
- B. This query is included in other organizations
- C. RDP connections will be blocked and classified as suspicious
- D. A security event will be triggered when the device attempts a RDP connection
Answer: D
NEW QUESTION # 18
Exhibit.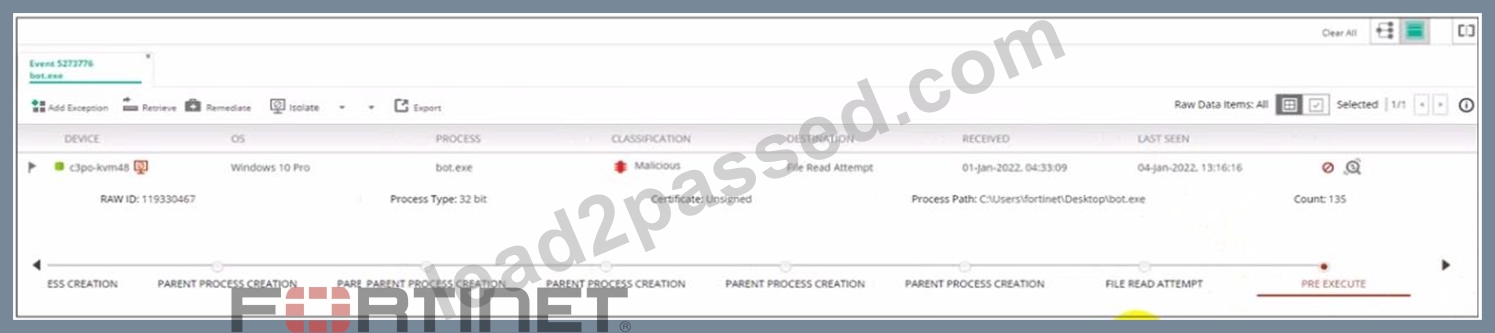
Based on the forensics data shown in the exhibit, which two statements are true? (Choose two.)
- A. The exfiltration prevention policy has blocked this event
- B. The forensics data is displayed m the stacks view
- C. An exception has been created for this event
- D. The device has been isolated
Answer: A,D
NEW QUESTION # 19
What is true about classifications assigned by Fortinet Cloud Sen/ice (FCS)?
- A. The core only assigns a classification if FCS is not available
- B. FCS revises the classification of the core based on its database
- C. FCS is responsible for all classifications
- D. The core is responsible for all classifications if FCS playbooks are disabled
Answer: B
NEW QUESTION # 20
A company requires a global communication policy for a FortiEDR multi-tenant environment.
How can the administrator achieve this?
- A. A local administrator creates new a communication control policy and shares it with other organizations
- B. A local administrator creates a new communication control policy and assigns it globally to all organizations
- C. An administrator creates a new communication control policy for each organization
- D. An administrator creates a new communication control policy and shares it with other organizations
Answer: B
NEW QUESTION # 21
Which scripting language is supported by the FortiEDR action managed?
- A. Perl
- B. Python
- C. TCL
- D. Bash
Answer: C
NEW QUESTION # 22
What is the purpose of the Threat Hunting feature?
- A. Identify all instances of a known malicious file or hash and notify affected users
- B. Execute playbooks to isolate affected collectors in the organization
- C. Delete any file from any collector in the organization
- D. Find and delete all instances ofa known malicious file or hash inthe organization
Answer: A
NEW QUESTION # 23
Refer to the exhibit.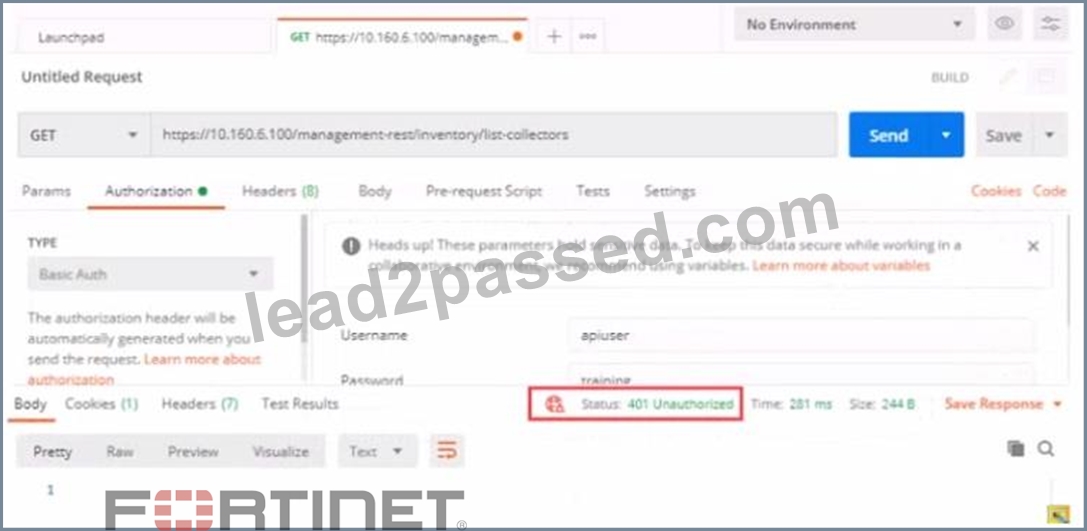
Based on the postman output shown in the exhibit why is the user getting an unauthorized error?
- A. API access is disabled on the central manager
- B. FortiEDR requires a password reset the first time a user logs in
- C. The user has been assigned Admin and Rest API roles
- D. Postman cannot reach the central manager
Answer: C
NEW QUESTION # 24
Refer to the exhibit.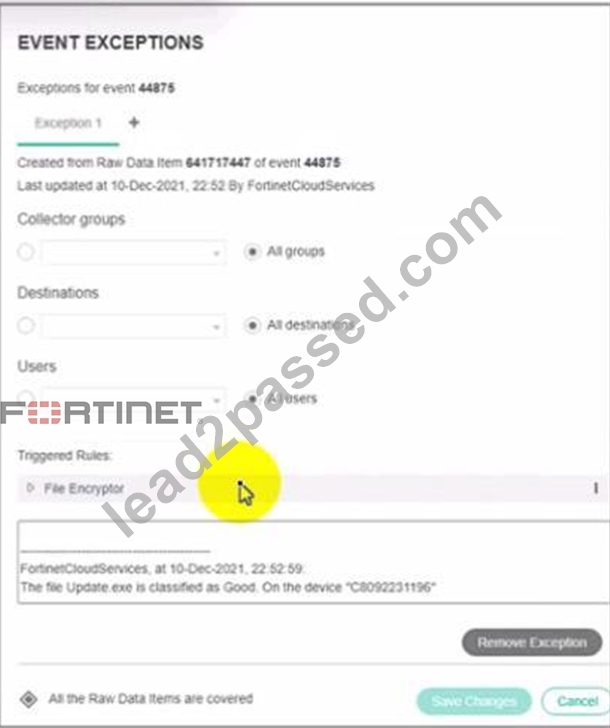
Based on the event exception shown in the exhibit which two statements about the exception are true? (Choose two)
- A. A partial exception is applied to this event
- B. The exception is applied only on device C8092231196
- C. FCS playbooks is enabled by Fortinet support
- D. The system owner can modify the trigger rules parameters
Answer: A,B
NEW QUESTION # 25
Which security policy has all of its rules disabled by default?
- A. Ransomware Prevention
- B. Execution Prevention
- C. Device Control
- D. Exfiltration Prevention
Answer: A
NEW QUESTION # 26
Refer to the exhibits.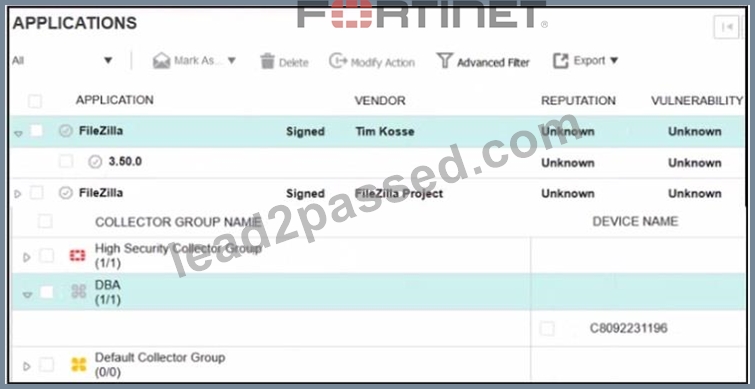
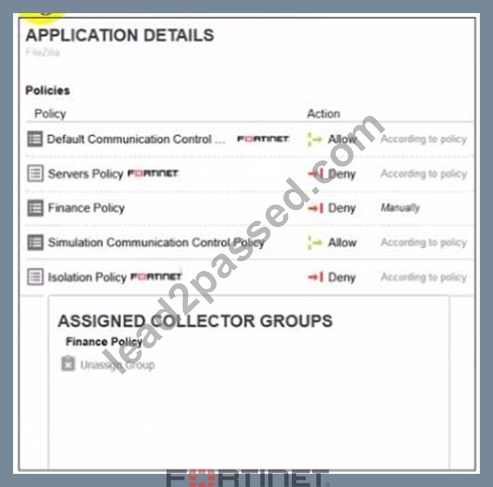
The exhibits show application policy logs and application details Collector C8092231196 is a member of the Finance group What must an administrator do to block the FileZilia application?
- A. Assign Simulation Communication Control Policy to DBA group
- B. Deny application in Finance policy
- C. Assign Finance policy to DBA group
- D. Assign Finance policy to Default Collector Group
Answer: A
NEW QUESTION # 27
Refer to the exhibit.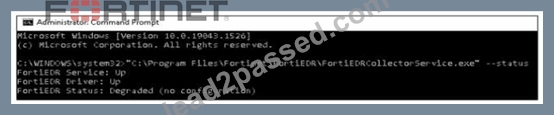
Based on the FortiEDR status output shown in the exhibit, which two statements about the FortiEDR collector are true? (Choose two.)
- A. The collector has been installed with an incorrect port number
- B. The collector device cannot reach the central manager
- C. The collector device has windows firewall enabled
- D. The collector has been installed with an incorrect registration password
Answer: A,B
NEW QUESTION # 28
FortiXDR relies on which feature as part of its automated extended response?
- A. Security Policies
- B. Playbooks
- C. Communication Control
- D. Forensic
Answer: A
NEW QUESTION # 29
......
Fortinet NSE5_EDR-5.0 certification exam covers a range of topics including advanced threat prevention and detection, Fortinet's advanced threat prevention technologies, FortiEDR deployment, and advanced threat response. Candidates are also tested on their knowledge of advanced threat analysis techniques and Fortinet's advanced threat intelligence capabilities.
NSE5_EDR-5.0 Sample with Accurate & Updated Questions: https://www.lead2passed.com/Fortinet/NSE5_EDR-5.0-practice-exam-dumps.html
NSE5_EDR-5.0 Exam Info and Free Practice Test | Lead2Passed: https://drive.google.com/open?id=1nX0MxJsHkDkAsjVTK3j5Z8nza7Yqas2u